ES
 IT
 PT
 DE
 NL


The gaming industry’s investment in cybersecurity has increased considerably in recent years, yet attacks against casino operators and their technology partners continue. High-profile incidents have demonstrated the potential financial and operational consequences of a breach, while the growing number of connected systems has created an increasingly complicated environment for security teams to manage.
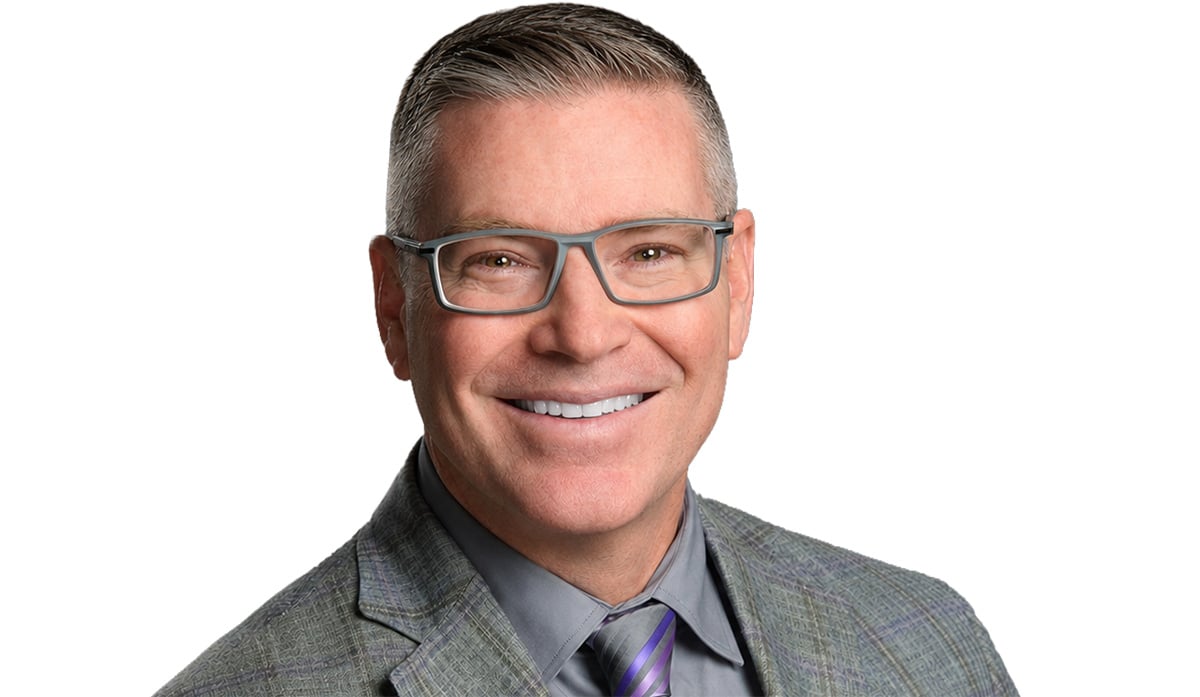
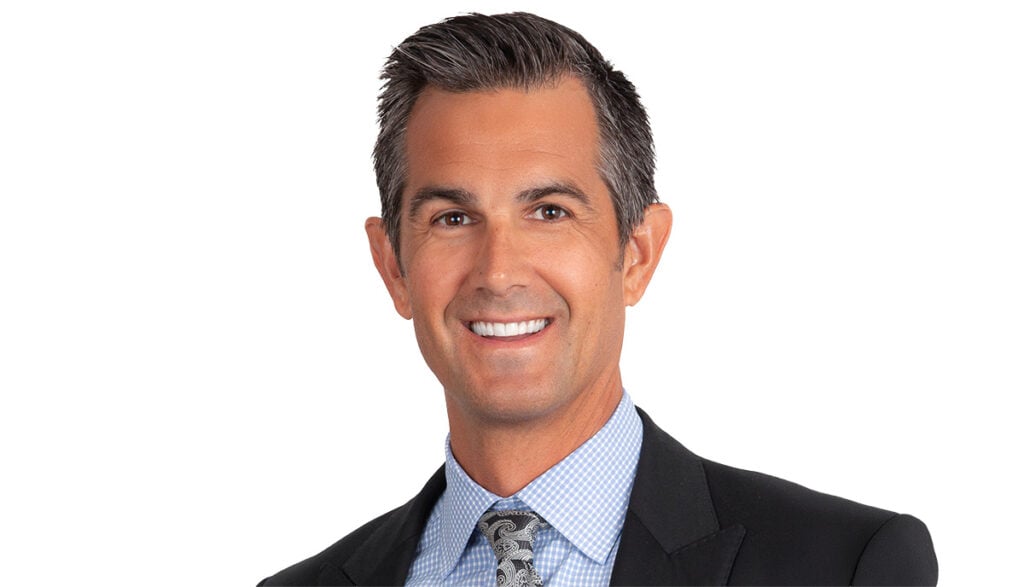
For David Elmore, Head of Commercial Services, North American Casinos at Gaming Laboratories International (GLI), one area stands out as requiring particular attention: third-party suppliers. “All the data that we’ve been gathering and seeing in the market indicates that third-party vendors are the number one vector for attack at this point,” Elmore told G3 during G2E in Las Vegas.
Elmore pointed to research from the Tribal Information Sharing and Analysis Center (Tribal-ISAC), which he said had surveyed approximately 300 respondents across around 90 tribal organisations. “About 80 per cent of the attacks are through third-party vendors,” he said, citing the research as evidence of the scale of the industry’s supplier security problem.
The challenge extends well beyond the gaming systems traditionally associated with casino operations. Today’s integrated resorts rely on interconnected hotel management platforms, point-of-sale terminals, building management systems, heating and ventilation equipment, payment infrastructure and an expanding range of applications designed to improve operational efficiency. Each system provides functionality and valuable business information. However, every connection also introduces another potential vulnerability.
Elmore points to the example of a casino that might have more than 180 different systems operating across its business. Integrating these technologies is already a considerable undertaking for IT departments, particularly when individual applications have been developed by different suppliers using different architectures. Ensuring that every component is secure, and remains secure as systems are updated and new functionality is introduced, adds another level of complexity.
The problem also extends beyond an operator’s immediate suppliers. A technology provider may rely on its own network of developers, cloud services, software libraries and specialist partners, creating additional dependencies that are not always visible to the casino purchasing the finished product. “It’s not just the one company you’re dealing with,” Elmore explained. “It’s every other supply chain, third-party that they work with to supplement everything they need to build their platform before it ever even gets to you.”
For operators, understanding those relationships is becoming an essential part of evaluating the risks associated with introducing new technology.
Building security standards for gaming
GLI has responded to these challenges by developing a cybersecurity framework specifically for the gaming industry. The GLI Gaming Security Framework (GLI-GSF) incorporates established principles from the Center for Internet Security (CIS) and the US National Institute of Standards and Technology (NIST), adapting them to the operational requirements of regulated gaming. Elmore explained that the initiative emerged from discussions with casino executives, technology leaders and regulators who wanted a more targeted approach than the broader security assessments commonly used across other industries.
Frameworks and assurance programmes such as SOC 2 Type II and ISO 27001 provide established methods of evaluating security controls, but Elmore argues that they do not necessarily address every challenge facing gaming operators with the specificity required. He compared the application of broad security standards to using a hammer when a more precise tool is needed, describing the limitations of applying an extensive general assessment to every gaming business.
GLI Secure’s approach was to identify the most relevant elements of established cybersecurity standards and work with industry stakeholders to develop controls addressing the threats encountered within gaming environments. The resulting framework includes common information security controls, technical security assessments and separate modules addressing vendor security, land-based gaming and online gaming. These distinctions reflect differences in how technology is deployed and managed across the industry, although Elmore stresses that the underlying exposure to cyberattacks is not confined to any particular sector.
Whether a company operates a land-based casino, an online gaming platform or a sportsbook, it depends on interconnected technologies that must be protected. The objective is to establish a common baseline against which operators and suppliers can assess their security arrangements, without requiring every organisation to undertake an unnecessarily broad or expensive assessment.
The supplier security problem
One of the principal developments arising from GLI Secure’s work is its Vendor Security Program, designed to address the difficulties operators face when assessing the security of third-party technology providers. Elmore described the existing process as cumbersome for both parties.
Casino operators routinely distribute extensive security questionnaires to prospective suppliers, asking them to demonstrate compliance with internal policies, technical requirements and insurance obligations. The supplier must dedicate resources to completing those assessments, often repeating substantially the same exercise for multiple customers. The operator must then review the responses and determine whether the supplier represents an acceptable risk. For companies supplying technology across numerous gaming jurisdictions, the administrative burden can become considerable.
GLI Secure’s Vendor Security Program provides independent assessments against gaming-specific requirements, allowing suppliers to demonstrate that their products and security practices have been evaluated through a recognised process. The programme combines security governance assessments, technical controls and penetration testing, examining both the supplier’s internal practices and the resilience of the technology being offered. The intention is to provide operators with a consistent basis for evaluating vendors while reducing duplicated assessments that can delay the introduction of new products.
Elmore emphasised that the objective is not to prevent innovation. “You want to ensure that you’re protecting yourself at a level where you’re not adding additional vulnerabilities, but you don’t want to be so restrictive that you’re not allowing in new technology.” That balance is becoming increasingly difficult to maintain.
Operators are under pressure to introduce new systems that improve customer experiences, increase operational efficiency and generate additional revenue. Suppliers, meanwhile, face considerable competition to bring their products to market. The danger is that security assessments become compressed as commercial deadlines take priority.
Elmore believes that the industry needs to recognise that a supplier’s existing vulnerabilities do not disappear when its technology is integrated into a casino’s network. Equally, an assessment completed during the procurement process cannot guarantee that a product will remain secure indefinitely.
Security cannot be a one-off exercise
The changing nature of cyber threats means operators must continually reassess their systems and suppliers. Elmore advocates regular internal vulnerability scanning, supported by independent assessments that help security teams identify weaknesses and remain informed about emerging threats. He suggested that operators should ideally undertake their own vulnerability assessments monthly, with external specialists potentially reviewing systems quarterly.
Such a programme does not necessarily require the same level of expenditure as a comprehensive external audit every time. Automated tools can identify known vulnerabilities and configuration weaknesses, while specialist assistance can help internal teams develop the expertise to interpret results and address problems. GLI Secure also supports operators in learning how to conduct these assessments themselves.
For Elmore, the important distinction is between security as a recurring operational responsibility and security as a compliance exercise completed at a particular point in time. A system that passes an assessment today may become vulnerable following a software update, the discovery of a new exploit or the integration of another application.
The increasing use of APIs to connect previously separate systems adds to this challenge. Although these interfaces are essential to modern gaming platforms, they also create additional routes through which attackers may attempt to access data or connected services. The responsibility for managing those risks ultimately sits with the operator, even when the vulnerable component originates from an external supplier.
Artificial intelligence changes the equation
Alongside third-party vulnerabilities, artificial intelligence is introducing another dimension to the cybersecurity challenge. Elmore believes the most immediate impact of AI is not simply the development of more sophisticated attacks, but the speed and scale at which malicious activity can be generated.
“Right now, you see 71,000 attacks per minute worldwide,” he said, warning that the volume could increase dramatically as AI-assisted attack tools become more widely available. “By 2027, that could be three to ten times as many attacks because of AI.”
Elmore’s prediction reflects his concern that AI will enable malicious actors to automate increasingly sophisticated attacks at a scale that conventional defensive approaches may struggle to manage. At the same time, defensive technologies are increasingly using AI to analyse network activity, identify suspicious behaviour and prioritise threats requiring investigation.
For large casino operators, where security teams may receive enormous volumes of alerts, this filtering process is becoming particularly important. Elmore described a future in which several layers of automated analysis could examine incoming activity before potentially serious incidents are escalated to human specialists. However, he believes human expertise will remain essential in determining whether an alert represents a genuine attack and deciding how an organisation should respond.
The challenge is compounded by attackers who establish a presence inside a network and deliberately avoid triggering security systems. Once inside, a sophisticated attacker may study an organisation’s policies, monitoring thresholds and access arrangements, allowing them to remain undetected while collecting information, moving between systems or increasing their privileges. The longer an attacker remains within a network, the greater the opportunity to understand its structure and exploit additional weaknesses.
Elmore also expressed concern about the rapid proliferation of AI tools, particularly as capabilities developed for legitimate purposes become available to malicious actors. He believes the industry needs to be prepared for a cybersecurity environment in which both attackers and defenders are deploying increasingly powerful automated technologies.
Who is responsible for cybersecurity?
Although IT departments remain responsible for implementing technical security controls, Elmore argues that cybersecurity cannot be treated exclusively as an IT function. Every employee with access to corporate systems has a role in protecting the organisation. Social engineering and phishing attacks remain significant threats, particularly when employees are working quickly and may not take the time to verify an unexpected email, link or request for information.
The IT department must establish appropriate policies, training and technical safeguards, while compliance teams help define the controls necessary to meet regulatory and organisational requirements. However, those arrangements depend on employees understanding and following the procedures. “It’s a responsibility of every single person, in every single department, to be aware of the attacks that are coming in,” Elmore said.
The issue also extends to the boardroom. Cybersecurity expenditure can be difficult to justify using the financial measures traditionally applied to commercial investments. A new gaming product, loyalty system or customer-facing application may offer a projected increase in revenue. Security investment is generally intended to prevent losses that have not yet occurred. Elmore believes this creates a persistent problem for operators attempting to allocate resources.
The financial justification for prevention may appear less immediate than the commercial benefits of introducing new technology, even though a serious cyber incident can have consequences far beyond the cost of the initial breach.
The cost of complacency
The attacks against MGM Resorts and Caesars Entertainment in 2023 demonstrated the potential disruption that cyber incidents can cause major gaming operators. However, Elmore said that although these incidents increased awareness, they did not generate the industry-wide response that some cybersecurity specialists had anticipated.
GLI Secure had expected the scale and publicity surrounding the attacks to prompt a more substantial reassessment of security arrangements. Instead, Elmore believes many organisations continued to approach cybersecurity through existing budgets and operational priorities. The implications are particularly significant for smaller casinos and tribal gaming operations, where a major incident may threaten not only the operator’s finances but also the communities and programmes supported by gaming revenues.
For tribal operators, casino income can provide funding for essential community services. A prolonged disruption or substantial financial loss can therefore have consequences extending well beyond the gaming floor. Elmore argues that cybersecurity should be considered part of protecting those wider responsibilities. There is also the question of customer confidence.
A casino that experiences a significant breach may face concerns about the protection of personal information, the security of financial transactions and the integrity of its operations. Even where an incident does not compromise gaming outcomes, the reputational consequences can influence how customers perceive the operator. Cyber insurance provides another consideration, but Elmore cautioned against treating insurance coverage as a substitute for effective security controls.
Policies commonly impose requirements concerning security procedures and risk management. Operators must understand those obligations and ensure their practices remain consistent with the conditions of their coverage. He also questioned whether cyber insurance would remain affordable for every operator if the frequency and financial consequences of attacks continue to increase.
The next 12 months
Asked which aspect of cybersecurity operators should scrutinise most closely over the coming year, Elmore returned to third-party suppliers. His recommendation is that operators examine their vendor relationships more thoroughly, establish appropriate baseline requirements and ensure that assessments continue after products have been deployed. GLI Secure’s Vendor Security Program is intended to support that process by providing a common approach to supplier assurance, while its Gaming Security Framework establishes controls that can be applied across different gaming environments. For Elmore, the commercial challenge is ensuring that cybersecurity keeps pace with the industry’s appetite for innovation.
Gaming operators are continually introducing technologies intended to improve efficiency, attract customers and generate revenue. Each development may bring substantial benefits, but it also requires consideration of how the technology connects to existing systems and what additional exposure it creates.
The industry’s experience of major cyberattacks has increased awareness, but Elmore remains concerned that preventative investment is not progressing quickly enough. He sees little reason to expect the threat environment to become less demanding over the next year, particularly given the increasing availability of AI-assisted attack tools and the continued expansion of interconnected systems. His central message is that operators should not wait until they experience an incident before treating cybersecurity as an essential business investment. The question is no longer simply whether a casino’s own systems are secure, but whether the organisation understands the vulnerabilities introduced by every company, application and service connected to its network. For an industry increasingly dependent on technology, that responsibility will only become more important.
Third-Party Vendors: the Weakest Links?
As casinos become increasingly dependent on interconnected technologies and third-party suppliers, cybersecurity is becoming a more complex challenge for the gaming industry. Speaking exclusively to G3 at G2E Las Vegas, David Elmore, Head of Commercial Services, North American Casinos at Gaming Laboratories International (GLI), explains why supplier vulnerabilities, artificial intelligence and the pressure to bring new products to market are placing greater demands on operators' security strategies.